Run agents that stay inside the lines.
Isolated sandboxes, scoped credentials, streaming tool calls and a full audit trail for every run.
Every run gets its own walls.
An agent run never shares memory, files or credentials with another. Everything it touches is written to the trace.
Agent run
Sandbox
Tools
Trace
From script to worker.
State between steps, typed tools, limits you set and a replay for every run.

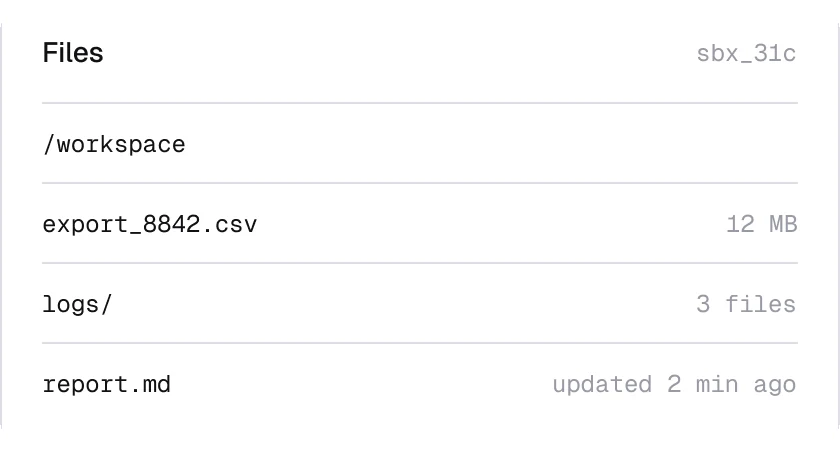
Persistent sandboxes
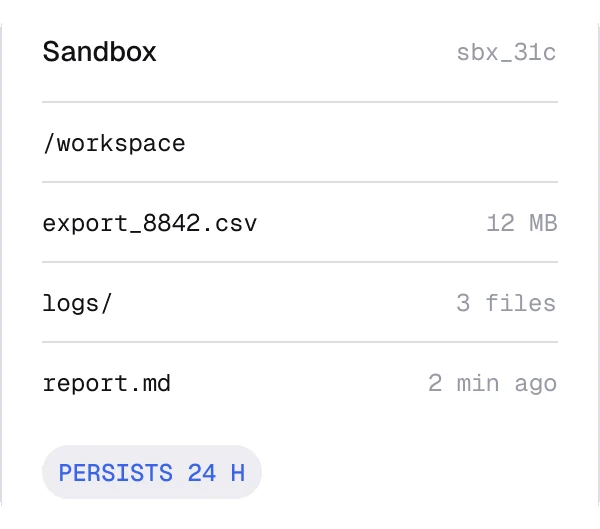
Filesystem and processes survive between steps for 24 hours, so long tasks pick up where they stopped.
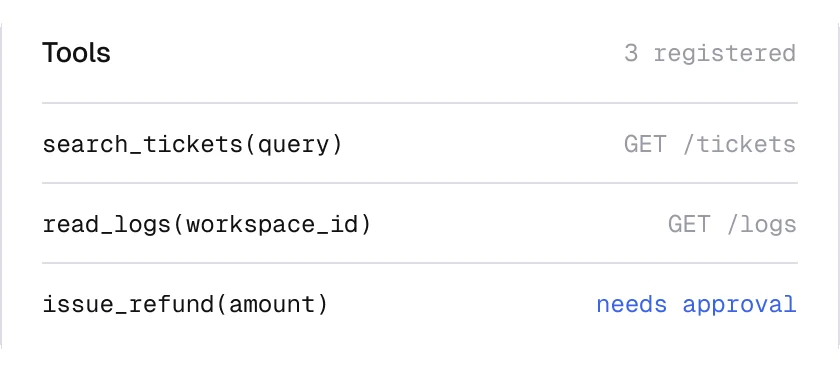

Tool registry
Any HTTP endpoint or Python function becomes a tool, with a generated and validated schema.

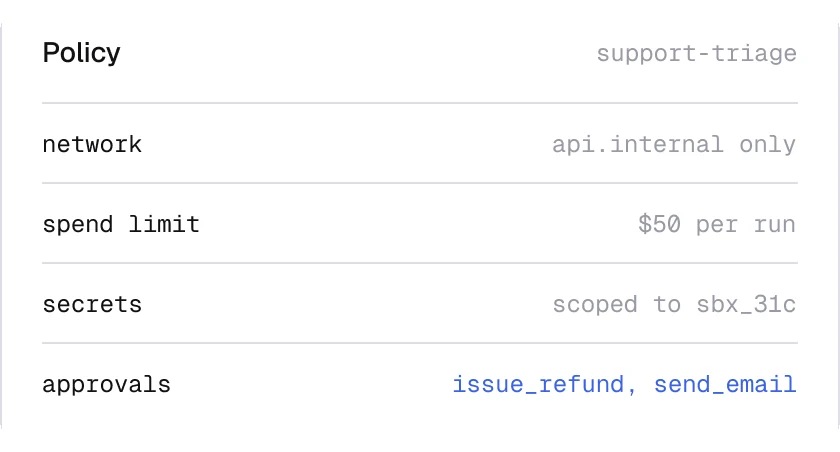
Guardrails
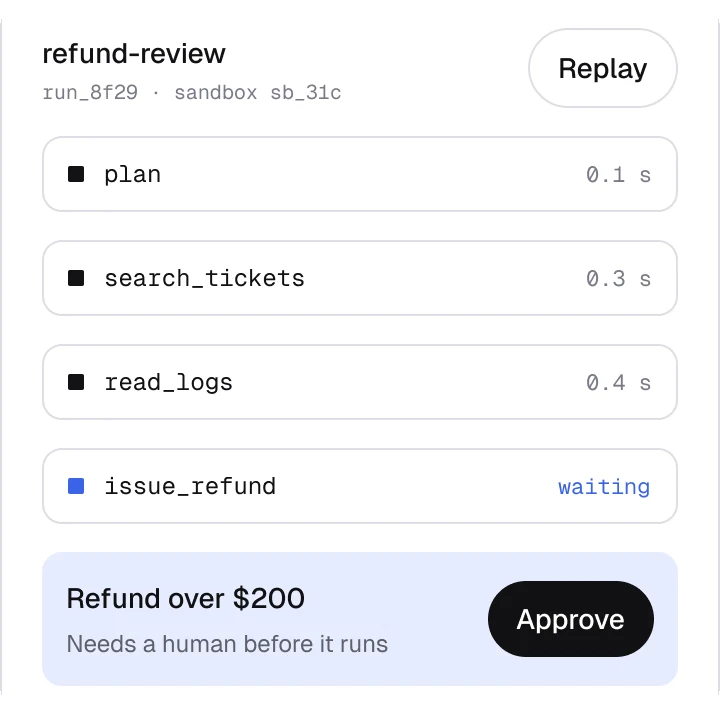
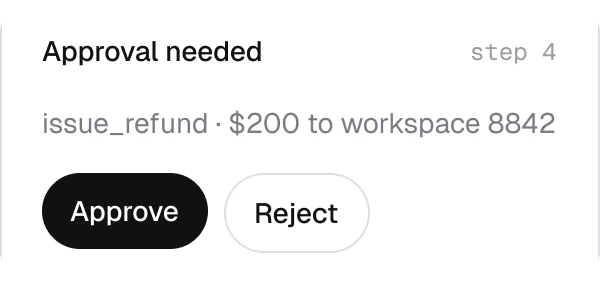
Network policy, spend limits and human approval steps, set per agent and enforced inside the sandbox.
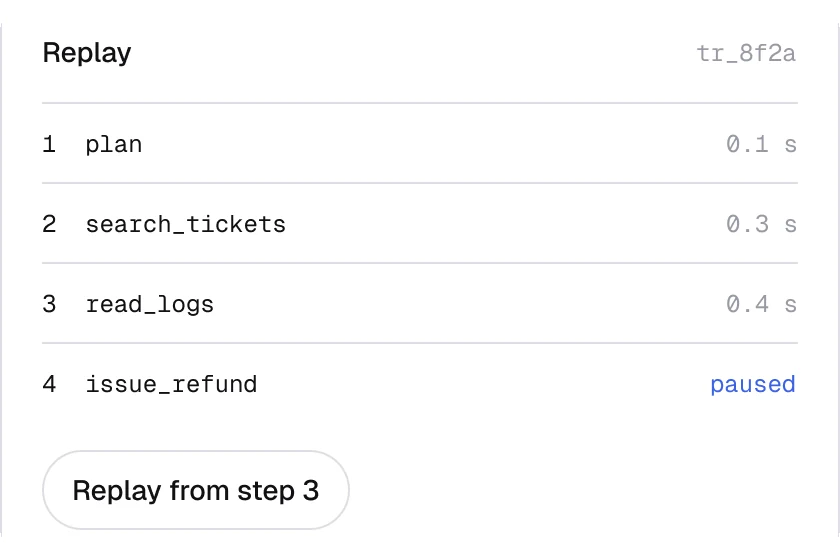

Replays
Every run can be replayed step by step, with the exact inputs and outputs it saw.
“Sandboxes gave us the thing we could not build ourselves: isolation we could explain to security.”
Agents, in plain terms.
How is a sandbox isolated?
Each run gets its own container with no shared memory, a private filesystem and a network policy you define.
Can agents call my internal APIs?
Yes. Register any HTTP endpoint as a tool and scope its credentials to the sandbox.
How do approvals work?
Mark a tool as approval required. The run pauses until someone approves it in the console or in Slack.
What does a run cost?
Sandbox minutes at $0.012 plus the tokens the agent uses. Approvals and replays are free.
Run your first agent in five minutes.
1M free tokens a month. No card, no sales call, production keys in two minutes.